From VMware exit to 3am pager. One senior team.
We migrate, build, and operate OpenShift and Kubernetes platforms for regulated, mission-critical, and edge environments — then govern how AI ships to them. Senior engineers only. No offshore hand-offs.
One team, from first assessment to day-two operations.
Start wherever you are. Every service hands off cleanly to the next — usually to the same engineers.
Migrate & build
Move, build, modernize
VMware → OpenShift Virt→Bare-metal platform builds→Federal & air-gapped→App modernization→Protect & govern
Recoverable, compliant, AI-ready
Data protection & DR→GitOps & secure delivery→Compliance as code→Migrate off VMware — or shrink it. Keep your VMs either way.
Broadcom changed the economics of VMware overnight. Move your whole estate, or run OpenShift Virtualization alongside vSphere and cut what you license. Either way, we move your virtual machines onto Red Hat OpenShift Virtualization with the Migration Toolkit for Virtualization — cold and warm migrations, network and storage mapping, and wave-based cutovers that keep workloads running. Done in production on bare metal with enterprise storage, including CJIS-scoped government environments.
- ✓Readiness assessment: inventory, dependency mapping, sizing, and a migrate-or-rebalance plan
- ✓Pilot migration proves the full path before production moves
- ✓Wave-based migration with MTV/Forklift, plus guest remediation (virtio, guest agent, boot fixes)
- ✓Software-defined storage and modern data protection built in, not bolted on
- ✓VMs and containers side by side — one platform, one operating model
Fixed scope · priced per workload or per cluster · most engagements continue into managed operations
Your platform, run by the people who'd build it.
We operate OpenShift and Kubernetes as a true extension of your team — the senior engineers who run your changes are the ones who answer your 3am P1. Today we run a 30+ cluster shipboard fleet plus shoreside clusters for a Fortune-500 enterprise.
- ✓24×7 coverage from named, US-based senior engineers — no shared NOC
- ✓Tiered SLAs with acknowledge, engage, and mitigate milestones
- ✓Upgrades, patching, scaling, backup/DR operations, and incident response
- ✓Clean Red Hat escalation when an issue is upstream
- ✓Transparent per-cluster pricing — no surprise change orders
Monthly · priced per cluster · Standard 24×7 and Enhanced 24×7 tiers
- 03:02Alert firesMonitoring pages the on-call rotation
- 03:05AcknowledgeA named senior engineer owns it — no shared NOC
- 03:11EngageHands on the cluster, Red Hat looped in if upstream
- 03:38MitigateService restored · RCA and fix to follow
OpenShift where the internet doesn't reach.
Most integrators can deploy OpenShift. Far fewer can deploy it fully disconnected, hardened to federal standards, in a classified facility. Our background spans USMC, DoD, FBI, and DHS engagements — and as an SDVOSB we bring the contracting access government work requires.
- ✓Air-gapped installs: Quay mirror registry, oc-mirror pipelines, agent-based deployment
- ✓DISA STIG hardening via the Compliance Operator, FIPS mode, continuous compliance
- ✓FedRAMP and DoD Impact Level readiness
- ✓Authorized supply chain: Red Hat Satellite, Iron Bank / Platform One
- ✓Cross-domain and media-transfer workflows for true air gaps
Fixed scope per enclave · SDVOSB set-aside eligible
Run containers where the network barely reaches.
Disconnected sites, intermittent links, hundreds of identical locations — that's where most platform teams struggle and where we're strongest. We design and operate containerized edge fleets with Podman, Quadlet, and pull-based GitOps, so every site stays consistent, self-heals, and updates safely. Built for maritime, retail, manufacturing, and any estate of remote sites.
- ✓Fleet architecture that survives intermittent and low-bandwidth links
- ✓Pull-based GitOps and image-mode delivery for atomic, rollback-safe updates
- ✓Consistent configuration and security posture across every site
- ✓Edge-appropriate WAF and end-to-end TLS — no heavyweight control plane
- ✓Centralized fleet management without per-site cluster sprawl
Monthly · priced per site or per fleet
The work that holds it all together.
Bare-metal OpenShift & Virtualization builds
Production OpenShift on your hardware — where the hard problems actually live.
- ›Agent-based, IPI, or UPI cluster deployment
- ›Portworx, Pure FlashArray, or ODF storage — RWX for live-migratable VMs
- ›VLAN/OVN, EgressIP, MetalLB, and NIC bonding
- ›Day-two runbooks tailored to your environment
Application modernization & containerization
We've containerized 150+ legacy apps off Windows onto a governed Kubernetes platform.
- ›Containerize legacy and Windows-hosted applications
- ›Build-scan-deploy pipeline built once, reused for every app
- ›A repeatable onboarding path your teams own
- ›Delivered in waves, so value lands early
Backup & disaster recovery for Kubernetes
A migrated VM without a backup is a liability. Tested, not assumed.
- ›Kasten K10, Trilio, and native snapshot workflows
- ›DR cluster architecture and build-out
- ›Recovery runbooks with tested restores
- ›On-prem and S3-compatible storage targets
GitOps & secure platform engineering
Declarative, auditable delivery for regulated Kubernetes — and ready for AI-proposed change.
- ›Argo CD and Red Hat OpenShift GitOps pipelines
- ›Fleet policy with Red Hat ACM and ACS
- ›Secure workflows for regulated and air-gapped sites
- ›AI-proposed changes governed by policy via TruStacks
Controls as engineering guarantees, not policy documents.
Separation of duties enforced as a technical control. Audit evidence generated automatically. Compliance encoded as policy-as-code instead of a binder nobody maintains — delivered for SOX-scoped financial systems and CJIS-scoped government environments.
- commitChange proposedby an engineer or an agent
- policyPolicy-as-codeOPA / Rego checks
- supply chainScan & signimage integrity, SBOM
- separationApprover ≠ authorenforced by the pipeline
- evidenceAudit evidencegenerated automatically
- releaseProductiondefensible by default
Two fixed-price ways to begin.
A short, scoped engagement that ends with a plan you can fund — and a clear view of whether we're the right team to execute it.
VMware Readiness Assessment
- ✓Inventory and dependency map of your vSphere estate
- ✓Target sizing on OpenShift Virtualization
- ✓Cost model for staying, rebalancing, or migrating
- ✓Wave plan with timelines and risks
Platform & DevOps Maturity Assessment
- ✓Scored baseline across tooling, process, structure, and security
- ✓A prioritized roadmap leadership can fund
- ✓Executive-ready findings — not a 90-page report
- ✓Quick wins separated from strategic investments
Production-proven, not PowerPoint-proven.
We've done the hard version.
Bare-metal OpenShift Virtualization migrations with enterprise storage, complex networking, and full day-two operations — in production, under real constraints.
Veteran-owned, federal-ready.
A background spanning USMC, DoD, FBI, and DHS. SDVOSB and NVBDC certified. Red Hat Partner. The access and depth government work requires.
Senior engineers, not hand-offs.
You work directly with the people who do the work — 24 years of DevOps, automation, cloud, storage, and container experience behind every engagement.
Governing what AI ships to production.
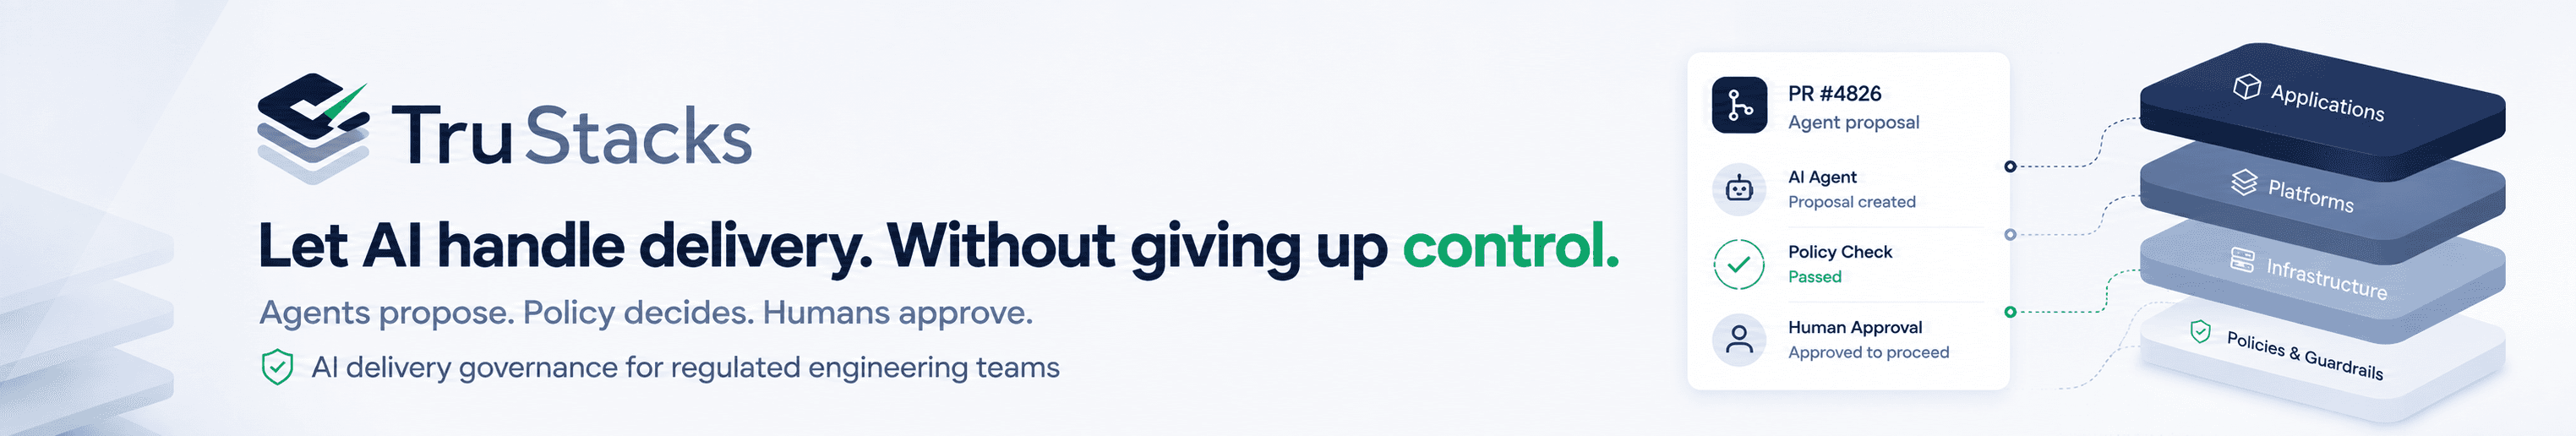
TruStacks is our AI delivery-governance platform: agents propose, policy decides, humans approve. Every change is checked against signed policy-as-code before a human reviews it — no autonomous path to production, by design.
Ready to ship like the AI era demands?
Escaping VMware or putting AI to work in your pipeline — a senior engineer will scope it with you. No sales sequence.